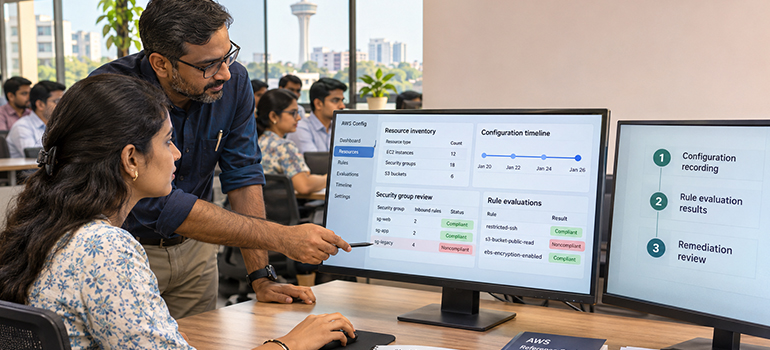
AWS Security Training Ahmedabad helps learners understand how AWS Config records resource settings and evaluates them against selected security requirements. Furthermore, configuration visibility helps administrators investigate changes that could affect their cloud environment. AWS Config provides useful evidence, but teams must interpret findings and address problems. Understanding this workflow connects cloud security concepts with practical administration responsibilities. Discuss relevant learning exercises with HighSky IT Solutions when exploring your training options.
What Is AWS Config?
AWS Config records configuration details for supported resources within your chosen recording scope. Additionally, it maintains historical information that helps administrators understand how resource settings changed. Teams can inspect recorded configurations and investigate relationships between supported cloud resources. This visibility supports troubleshooting, security reviews, and evidence collection during internal audits. However, teams should confirm recording coverage before assuming the service tracks every resource.
How Does AWS Config Track Configuration Changes?
When recording begins, AWS Config discovers supported resources within the configured scope. Next, it creates configuration items containing information about those resources and their settings. As recording continues, it captures relevant changes according to the selected recording configuration. These records help administrators compare previous settings with more recent resource configurations. Recording starts from service setup rather than reconstructing every change before activation.
What Can Configuration History Tell You?
Configuration history helps administrators examine what a recorded resource looked like previously. For example, a security review might investigate earlier rules within a recorded security group. Reviewing those settings can help teams understand when access conditions became different. Teams should connect this evidence with other relevant records before drawing conclusions. Configuration history supports investigation, but it does not independently explain every operational decision.
How Do AWS Config Rules Evaluate Security Settings?
AWS Config rules compare resource configurations with conditions that your team defines. Furthermore, evaluations identify whether resources satisfy the requirements within each rule’s scope. Depending on the rule, evaluations respond to configuration changes or run periodically. A noncompliant result indicates that a resource failed the selected evaluation conditions. Administrators should inspect the relevant rule before deciding what the finding means.
How Do Managed Rules Differ From Custom Rules?
AWS provides managed rules that teams can select for supported evaluation requirements. However, organisations may need custom rules when existing checks do not match their policies. AWS supports custom evaluation approaches using Lambda functions or Guard policy definitions. Choose the approach according to your requirement, available expertise, and maintenance responsibilities. Learners comparing AWS Certification Training Courses in Ahmedabad should understand both options before attempting complex exercises.
What Does a Noncompliant Resource Actually Mean?
A noncompliant result describes a mismatch between resource settings and a particular rule. Therefore, teams should avoid treating every finding as proof of a security incident. Review the resource, rule parameters, business purpose, and any approved exception carefully. A compliant result also does not guarantee complete protection against every possible threat. Effective security reviews combine configuration checks with other controls and informed human judgement.
How Can You Practise AWS Config With a Simple Exercise?
Choose a supported resource and define one clear requirement within a training environment. Next, record its configuration and select an appropriate rule for that requirement. Inspect the evaluation result and explain which settings influenced the reported outcome. Make an authorised test change, then review the resulting history and evaluation. Ask HighSky IT Solutions how proposed assignments develop this observation and reasoning process.
Does AWS Config Automatically Fix Every Security Problem?
AWS Config supports remediation, but administrators must configure the appropriate actions separately. Additionally, teams can choose manual or automatic remediation for supported operational requirements. AWS Config remediation uses AWS Systems Manager documents to define the intended actions. Review permissions, inputs, and possible application effects before allowing changes to run. Detecting a configuration mismatch does not mean the service automatically corrects it.
Why Should You Review Remediation Before Automating It?
A configuration change can affect applications, users, integrations, or other dependent resources. Therefore, test the proposed correction and confirm that it preserves necessary business functions. Define who reviews failures and how the team handles unexpected operational effects. Keep clear records explaining why the remediation exists and what it changes. Automation works more reliably when teams understand the intended outcome and its limitations.
How Do Conformance Packs Organise Related Checks?
Conformance packs group AWS Config rules and remediation actions into one deployable collection. Furthermore, teams can use these collections to organise checks around shared policy objectives. A collection helps administrators manage related requirements without treating each rule independently. However, deploying a pack does not automatically prove compliance with every external obligation. Review its contents and scope against the requirements your organisation actually follows.
Can AWS Config Help Teams Review Multiple Accounts?
An aggregator collects configuration and compliance data from multiple accounts and Regions. Additionally, it provides a central view that helps teams inspect distributed environments. The aggregator offers read-only visibility rather than direct access to modify source resources. Administrators must use suitable separate processes when they need changes within those accounts. Understanding this boundary helps learners distinguish central reporting from operational control.
What Should You Check Before Enabling Broad Configuration Recording?
Define which resources and Regions require visibility before choosing your recording scope. Moreover, review recording frequency, expected activity, and relevant service charges before expanding coverage. AWS Config offers recording choices that can affect the detail and timing available. Confirm that your chosen approach supports the investigations and evaluations you require. Include these planning questions when comparing AWS Security Training Ahmedabad learning activities.
What Should a Practical AWS Config Review Include?
A Configuration Security Checklist
A useful review connects recording coverage, meaningful rules, investigation, and clearly assigned responsibilities. Furthermore, administrators should understand what each evaluation checks before relying on its status. Document approved exceptions and review them when business needs or configurations change. Check whether someone receives findings and follows them through to a verified outcome. Discuss this complete workflow with HighSky IT Solutions when reviewing practical course content.
- Confirm the resource types, accounts, and Regions that require configuration visibility.
- Select rules that match clear requirements rather than collecting unexplained compliance results.
- Review rule scope and parameters before interpreting any reported configuration mismatch.
- Assign responsibility for investigation, approved exceptions, remediation, and verification after changes.
- Test proposed remediation before allowing it to modify important operational resources.
- Review recording choices, access permissions, and service costs as your environment grows.
Turn Configuration Records Into Clear Security Decisions
AWS Config helps teams understand resource settings, review changes, and evaluate selected requirements. Therefore, combine its findings with careful investigation and practical processes for resolving problems. Compare AWS Certification Training Courses in Ahmedabad through exercises covering recording, evaluation, and remediation decisions. Discuss your learning goals with HighSky IT Solutions and request relevant syllabus details. Strong cloud security learning explains both what a service reveals and what requires further judgement.
FAQs
AWS Config records supported resource configurations and evaluates selected requirements; discuss practical configuration review exercises with HighSky IT Solutions.
AWS Config connects configuration history with policy evaluations; ask HighSky IT Solutions how proposed assignments develop these practical skills.
Rules evaluate resource settings against defined conditions; discuss rule scope, parameters, and result interpretation with HighSky IT Solutions.
Remediation requires separate configuration and suitable permissions; ask HighSky IT Solutions about manual and automatic remediation learning exercises.
Managed rules provide predefined checks, while custom rules address specific requirements; discuss suitable examples with HighSky IT Solutions.
Recording does not reconstruct complete earlier configurations; ask HighSky IT Solutions how practical exercises explain history coverage and limitations.
Compare recording, rules, configuration history, remediation, aggregation, and practical assessments when discussing course content with HighSky IT Solutions.
Aggregators provide central configuration and compliance visibility; discuss their read-only role and source coverage with HighSky IT Solutions.
Compliance applies to selected rule conditions, not every threat; discuss broader security assessment principles with HighSky IT Solutions.
Ask HighSky IT Solutions about prerequisites, practical account access, recording costs, rule exercises, remediation testing, and trainer feedback.